Tag: EPrivacy
All blog posts with this tag.
- Nov 2, 2026
Digital Omnibus and cookies: proposals versus rules in force
On 21 October 2026, the Council of the European Union agreed its position on a proposal to simplify the EU's digital legal framework. Its announcement included clearer or additional purposes for which consent to certain cookies would not be required, citing audience measurement among the examples. For a business choosing analytics software, this sounds consequential. Should it change its consent interface today, switch tools or wait for a broader exemption? A negotiating mandate is not the same thing as legislation already in force. As of 2 November 2026, file 2025/0360(COD) is still progressing through the ordinary legislative procedure. The Council has agreed a position, while the European Parliament's legislative record reports that committee-level action is still awaited. No general exemption can be inferred from this stage. Three legal states that must not be conflated Rules currently applicable In France, Article 82 of the Data Protection Act governs certain trackers within the ePrivacy framework. The CNIL explains that narrowly scoped audience-measurement tools may qualify for a consent exemption under specific conditions. That is not a universal exemption for analytics. Purposes, implementation and information practices matter. Advertising attribution, cross-site identification and broader marketing uses should not be treated as if they were automatically part of strict audience measurement. Operationally, document actual fields, destinations, retention, purposes and configuration before taking a compliance position. The Digital Omnibus proposal The European Commission proposed a package of digital simplifications in November 2025, including proposed amendments to the ePrivacy Directive and GDPR. On 21 October 2026 the Council adopted a negotiating mandate. Its statement proposes retaining cookie rules in the ePrivacy framework while clarifying and expanding certain purposes not requiring consent. It cites service provision, audience measurement and device security as examples. The announcement alone does not define every possible analytics implementation as equivalent. Exact conditions, transition provisions and implementation dates depend on a final act that does not yet exist. A possible future legal regime Parliament must establish its position and negotiations between the institutions must conclude. Provisions may change substantially before adoption. A reliable internal tracker should therefore separate rules currently applicable, the initial proposal, the Council's position, Parliamentary steps, and eventually final published law. What the Council's statement actually covers The October Council release addresses multiple areas: personal data, cookies and ePrivacy, incident reporting and other digital rules. It is not solely an analytics proposal. For cookies, the Council describes keeping the ePrivacy regime while broadening or clarifying certain exceptions. Its examples include supplying a service, audience measurement and device security. A headline claiming that "Europe abolished cookie banners" would therefore go well beyond the evidence. Some uses may become simpler in the future without every tracking purpose receiving identical treatment. Privacy, security and transparency duties do not automatically vanish because one legal requirement related to terminal-device tracking is revised. Why analytics teams need to separate purposes An organisation operating five properties rarely collects data for one purpose only. It may analyse audience, conversions, technical incidents, content engagement, campaigns and authenticated product activity. The umbrella word "analytics" hides material distinctions. Qualify each activity before deciding on configuration or a consent framework.Proposed use Decision questionWebsite audience measurement Is it confined to the publisher's measurement needs?Technical troubleshooting Which information is essential to identify the problem?Marketing conversion events Do purposes go beyond strict audience measurement?Advertising attribution Are data shared, joined or used for targeting?Cross-domain analysis Are individual activities linked between properties?The same vendor may offer multiple configurations. Provider name or cookie absence does not settle the legal analysis. A decision checklist that works before reform Inventory the actual technology List scripts, pixels, storage mechanisms, events and network destinations. Separate strictly scoped audience measurement from broader marketing, product and advertising use. Our website tracker audit can help identify technical components; supplier documentation and contractual terms remain important. Describe each purpose plainly "Improve the user experience" does not necessarily distinguish basic statistics from conversion marketing or individual personalisation. Write the business decision each operation is intended to support and the minimum data needed. If a tool has several collection modes, document what each actually enables. A mode name is not evidence. Verify deployed settings Vendor documentation about an exemption-eligible configuration is not proof that a particular website uses it. Inspect outgoing requests, identifiers, settings and recipients. The CNIL's materials emphasise the importance of practical conditions and documentation. General claims of approval should never replace a site-specific review. Keep responsibilities and evidence Record the approved configuration, notice version, responsible persons and review date. Multi-site organisations need to know who can add events, alter collection settings or install a new third-party script. This is as much an operational governance problem as a legal one. Monitor the actual legislative outcome Use the European Parliament's Legislative Observatory and EUR-Lex rather than commentary alone. Once a final act exists, assess its conditions, commencement dates and implementation implications before changing systems. Should a team postpone analytics selection? Not necessarily. Business needs exist now: understandable site trends, shared reporting, restrained collection and reliable technical configuration. Waiting for uncertain legislation can delay those improvements without producing better evidence. Prefer tools whose configuration is inspectable, data flows are documented and purposes can be kept separate. Do not buy a promise about future law. Evaluate what the supplier can demonstrate today. What privacy-first analytics can realistically offer Pomelo's privacy-first approach centres on limited collection, clear governance and measurement without a measurement cookie by default. That can be relevant to a team's choices, but it does not justify claims such as "no banner in all circumstances" or "automatically exempt". Review actual purposes, configuration and applicable rules. A possible future reform should not be treated as a product feature. What to watch next The consequential signals are progress in Parliament on 2025/0360(COD), any interinstitutional agreement and publication of final law with dates of application. National and European regulatory guidance may subsequently clarify operational questions. Until then, the CNIL's existing material remains an important reference for audience-measurement configurations in France. Communicate legislative uncertainty inside the organisation Regulatory announcements can create different expectations. Marketing hears "fewer banners"; engineering imagines simpler configuration; the data-protection lead wants to know the exact legal scope. These reactions are not necessarily opposed, but they concern different decisions. Use a short review with three columns. The first lists requirements already applicable to each site, referencing the CNIL's current guidance and the actual deployment. The second records legislative proposals and negotiating positions with official sources and dates. The third lists possible implementation changes that should remain on hold until a final applicable basis has been verified. That format prevents two opposite mistakes. An organisation should not defer all analytics improvements simply because future legislation might change. Nor should it switch off a consent mechanism on the assumption that a proposed amendment will eventually become law in its current wording. Multi-site teams should coordinate their interpretation while preserving property-specific decisions. A public blog, a contact form and an authenticated product can have different processing purposes, despite sharing an analytics supplier. The review record should show why each configuration was chosen rather than copying one site-wide rule everywhere. Revisit the record on a genuine procedural milestone, not every time a commentary article repeats an old proposal. Why identical terminology can hide different configurations Even after a reform, teams will still need to inspect what software actually does. Two products labelled "analytics" may use different identifiers, retention periods or data recipients. Within one product, a change from basic traffic statistics to campaign attribution may alter purposes and data flows. That is why procurement documents should identify the configuration being assessed, not simply the product name. Record the event categories, storage mechanisms, sharing arrangements and technical controls. If a vendor changes defaults, review whether the legal interpretation still matches the deployment. This operational discipline is valuable even without new legislation: it reduces the chance that a later website redesign, agency script or marketing integration quietly expands the collection scope beyond what the original decision covered. Conclusion: decide under the rules in force The Council's 21 October announcement is a meaningful policy development, not a change that automatically takes effect. It opens a negotiating stage. The most durable preparation is clear documentation: separate purposes, useful events, limited data, known recipients and accountable configuration owners. Those practices benefit the organisation under current and future rules. FAQ Did the Digital Omnibus end analytics consent requirements? No. As of 2 November 2026, the Council's position is a negotiating step, not a final general exemption. Does the Council mention audience measurement? Yes. Its statement includes audience measurement among examples of purposes to be clarified or broadened. The final legal scope remains subject to the legislative process. Can a business remove cookie banners immediately? Not on the basis of this announcement alone. Actual trackers, purposes and currently applicable law must be reviewed. Where can the process be followed? The official file 2025/0360(COD) is available through the European Parliament's Legislative Observatory and EUR-Lex. SourcesCouncil of the EU, Digital Omnibus position, 21 October 2026 European Parliament, procedure 2025/0360(COD) EUR-Lex, procedure 2025/0360/COD CNIL, audience measurement consent conditions CNIL, law on cookies and trackers
Analytics consent: what to verify before promising “no cookie banner”
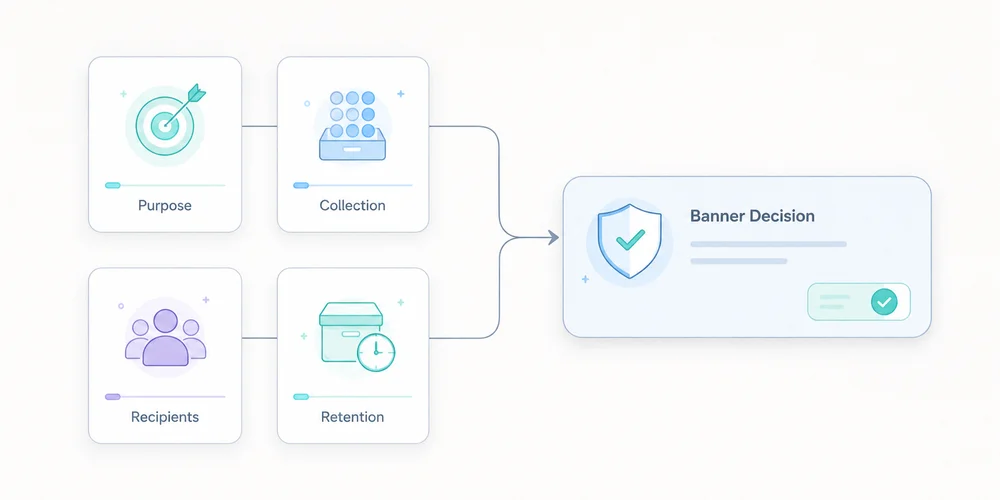
“Cookieless analytics” is often shortened to “consent-free analytics” and then to “no cookie banner”. Those statements are not equivalent. A tool can avoid HTTP cookies while reading or writing information on a device through another mechanism. A product may offer a limited audience-measurement configuration while other modules require a different assessment. And even when analytics fits a strict framework, videos, support widgets, advertising pixels or embedded forms elsewhere on the site may still require consent. The right question is not, “Is the tool cookieless?” It is:Which trackers and processing operations are actually deployed on this site, in this configuration, for which purposes and under which conditions?This is an assessment framework, not legal advice. It must be adapted to the countries, uses and setup involved. Do not confuse three layers 1. Storage or access technology A cookie is one technique. The ePrivacy framework more broadly addresses storing information on a user's terminal or accessing information already stored there, as transposed in national law. Local storage, SDKs, pixels, fingerprinting mechanisms and other terminal access can therefore raise consent questions without a traditional HTTP cookie. Cookieless is a technical characteristic, not a complete legal classification. 2. The ePrivacy tracker regime In France, Article 82 of the Data Protection Act implements the tracker rules. The general principle is prior information and consent for covered operations, with exceptions including operations strictly necessary for a service expressly requested. The CNIL also describes conditions under which certain audience-measurement trackers may fall within an exemption. This is a narrow framework, not a general exemption for all analytics. 3. Personal-data processing under the GDPR Even when a terminal operation does not require ePrivacy consent in a particular configuration, GDPR duties can still apply if personal data are processed. Purposes, legal basis, transparency, minimisation, retention, recipients, transfers, security and rights may still need to be documented. No banner does not mean no processing or no information. The French limited audience-measurement conditions The CNIL states that, to remain strictly necessary for the service and potentially fall within the described exemption, trackers must in particular:be strictly limited to measuring the audience of the site or app; operate exclusively on behalf of the publisher; produce anonymous statistics only; avoid combining the data with other processing; avoid transmitting non-anonymous data to third parties; avoid global tracking across websites or apps.The CNIL also recommends informing users, limiting tracker lifetime, for example to thirteen months without automatic extension, retaining collected information for no more than twenty-five months, and reviewing those periods. Each condition matters. Strictly limited purpose Technical performance, viewed content and navigation problems may fit the described logic. Advertising audiences, CRM enrichment, ad personalisation and cross-service tracking do not share the same purpose. One product interface may offer both. Audit the enabled feature, not only the vendor name. Exclusively for the publisher The provider should not turn the collection into data for its own targeting, profiling or incompatible cross-client measurement. Review the contract, product documentation and subprocessors. A marketing statement is not enough. Anonymous statistics “Anonymous” is a demanding word. Removing a name, truncating an IP address or hashing an identifier does not automatically create anonymity. If a signal still distinguishes or connects a person, use cautious terminology. Ask the vendor to explain transformations and re-identification risk. No global cross-site tracking A shared identifier used to deduplicate people across properties changes the scope. This matters for groups and agencies consolidating audiences. A multi-site dashboard can aggregate indicators without requiring a cross-site person identifier. The checklist before any no-banner promise 1. Inventory the whole site Do not begin and end with analytics. Include:analytics; tag managers; embedded video and maps; support chat; forms; fraud prevention; experimentation; session replay; advertising; social widgets; security and CDN tooling; partner scripts; mobile SDKs where relevant.Run a tracker audit before and after each consent choice, across several pages and journeys. Audience-only analytics does not neutralise an advertising pixel elsewhere. 2. State real purposes For every component, state what it enables:aggregate audience statistics; campaign analysis; personalisation; advertising; security; interaction recording; support; product experimentation.“Improve the service” is too broad to govern a configuration. 3. Identify terminal operations Document cookies, local storage, session storage, cache identifiers, SDKs, pixels, device characteristics, consent signals and withdrawal. A scanner showing no cookies does not close the assessment. 4. Inspect collected data and transformations The data collection summary should answer:Is the IP address received, used and stored? Is the full URL transmitted? Is the user-agent raw or reduced? Is a visitor identifier created? Is it stable across days or sites? Are UTM parameters retained? Can free-form events contain text? Which data are aggregated? At what point can a record no longer single someone out?An “anonymous mode” that nobody can explain is not evidence. 5. Review vendor use Ask whether the vendor:acts only as a processor for this collection; reuses data for its own purposes; combines data between customers; produces benchmarks from individual-level data; trains another product; sends data to subprocessors; makes international transfers.Benchmarking can sometimes be designed on separated aggregate data. It still needs to be understood. 6. Verify the exact configuration Documentation may say “can be configured to meet the criteria”. That does not mean your default account does. Keep evidence of:configuration export or screenshots; script version; collection parameters; disabled modules; allowed domains; retention; sharing options; verification date; owner.The CNIL tells publishers to request documentation and operating instructions from providers. 7. Review retention Separate tracker or identifier lifetime, raw events, statistics, technical logs, backups and exports. Test automated deletion. A dashboard retention setting may not cover files exported by your team. 8. Inform visitors Even when consent is not required for a strictly framed measurement setup, the CNIL recommends informing users, for example in the privacy notice. Depending on context, explain purpose, relevant data, general operation, duration, provider, recipients, rights, contact and relevant transfers. “We use privacy-friendly analytics” is not enough. 9. Test refusal and withdrawal Where part of the stack relies on consent:covered trackers must not start before the choice; refusal must follow applicable interface requirements; withdrawal must have an effect; the signal must reach all relevant tags; new pages and components must respect the choice.Test behaviour, not only the CMP appearance. 10. Validate and retain the assessment The controller makes the final decision, with DPO or legal support where appropriate. Record:countries; purposes; inventory; criteria reviewed; vendor evidence; configuration; tests; residual risks; date and owners; review triggers.The answer may differ for a French corporate site, an authenticated app and an international property group. Cookieless, consent mode and no banner Cookieless The term can mean no persistent cookie, no cookie in one mode, alternative storage, identifier-free events, server-derived identifiers or simply no advertising cookie. Ask for the technical definition. Consent mode A consent mode communicates user choices to tags and can change their behaviour. Depending on the product and setup, signals may still be sent without advertising cookies. It helps implement a decision. It does not decide whether no-consent collection is legally permitted, and it does not turn advertising into strictly necessary measurement. No banner This statement can only be assessed across the complete site. It may be reasonable when no non-essential component runs before consent and the audience measurement genuinely meets the applicable framework. It is misleading when based only on the absence of an analytics cookie. Claims to avoidabsolute GDPR or legal-compliance claims; blanket consent-exemption claims; claims that cookie-free analytics automatically remove every banner; claims of official CNIL certification; claims of official CNIL approval; “No personal data” “No legal assessment required”The CNIL explicitly states that a solution cannot present itself as certified or approved by the authority merely because of the audience-measurement self-assessment. More accurate wording includes:“cookieless by default”; “designed for minimal collection”; “can be configured for limited audience measurement”; “exemption depends on purposes, configuration and context”; “users remain informed”; “the complete site stack must be audited”.Precision protects credibility as well as compliance. When a banner remains necessary Depending on applicable law and configuration, consent is generally still relevant for:personalised advertising; retargeting; ad-network sharing; cross-site tracking; profile enrichment; some session-replay uses; non-essential personalisation; third-party embeds with non-essential trackers; analytics beyond a limited measurement purpose.The existing guide to session replay and the CNIL consultation explains why detailed behavioural recording should not be treated like aggregate audience statistics. A simple decision process Case A: strictly limited measurement Minimal collection, no cross-site tracking, no vendor reuse, anonymous statistics, controlled retention, information and documentation. Action: assess and document the local framework, then inspect the rest of the site. Case B: enriched analytics after consent The team wants detailed events, advanced attribution or more persistent identifiers. Action: block the relevant capabilities until consent, transmit the choice correctly and document the processing. Case C: mixed stack Audience measurement runs by default; marketing uses are enabled only after consent. Action: separate the purposes technically, prevent reporting changes from silently expanding collection, and test every transition. Clear separation is more credible than one setting claimed to fit every use. Conclusion A no-banner promise cannot be inferred from “cookieless”. It follows from an assessment of the complete site, purposes, terminal operations and configuration. Before communicating, verify:every component; purposes; terminal access; data and identifiers; vendor use; configuration; retention; transparency; consent behaviour where applicable; the documented decision.The result may be an audience-measurement-only stack, a consent-based marketing stack, or a clearly separated combination. Quality comes from the distinction, not the slogan. FAQ Is cookieless analytics automatically exempt from consent? No. Assess other terminal operations, purposes, data, identifiers and applicable national law. Cookieless is a technical feature, not a legal conclusion. Does the CNIL certify exempt analytics tools? No. The CNIL provides criteria and a self-assessment tool but says providers cannot present that self-assessment as official certification or approval. Can visitors be informed without a banner? Yes, when consent is not required for the relevant collection, information can be provided in a privacy notice or another appropriate location. It must remain clear and accurate. Do UTM tags prevent an exemption? Not automatically, but their use and combination must remain compatible with the limited purpose, minimisation and absence of cross-site tracking. They must never contain personal data. Who decides whether the site can operate without a banner? The controller makes and documents the decision, supported by a DPO or legal adviser where needed. A vendor alone cannot guarantee the answer for every site. SourcesCNIL, Audience-measurement cookies and consent conditions CNIL, What does the law say about cookies and trackers? Directive 2002/58/EC on privacy and electronic communications EDPB, Guidelines 05/2020 on consent EDPB, Guidelines 2/2023 on the technical scope of Article 5(3) ePrivacy

Just the right measure, for all your websites.
Pomelo is opening gradually. Join the first teams measuring right and help shape what comes next.